> ## Documentation Index
> Fetch the complete documentation index at: https://docs.kubestacks.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Signing in to your team's KubeStacks
> Open your team's KubeStacks, sign in, and see and change what your own account may, with nothing to install.
When KubeStacks runs in a cluster, it's a web page. Open the address your team gave you, sign in, and the cluster's overview opens. Everything you see, and every change you can make, is what your own Kubernetes account allows: KubeStacks never gives anyone more.
## Sign in
How you sign in depends on how your team set KubeStacks up. The sign-in page shows the right way.
Choose **Sign in with …** (your company's provider, like Okta or Google), and sign in there as you usually do. You come back to KubeStacks, signed in.
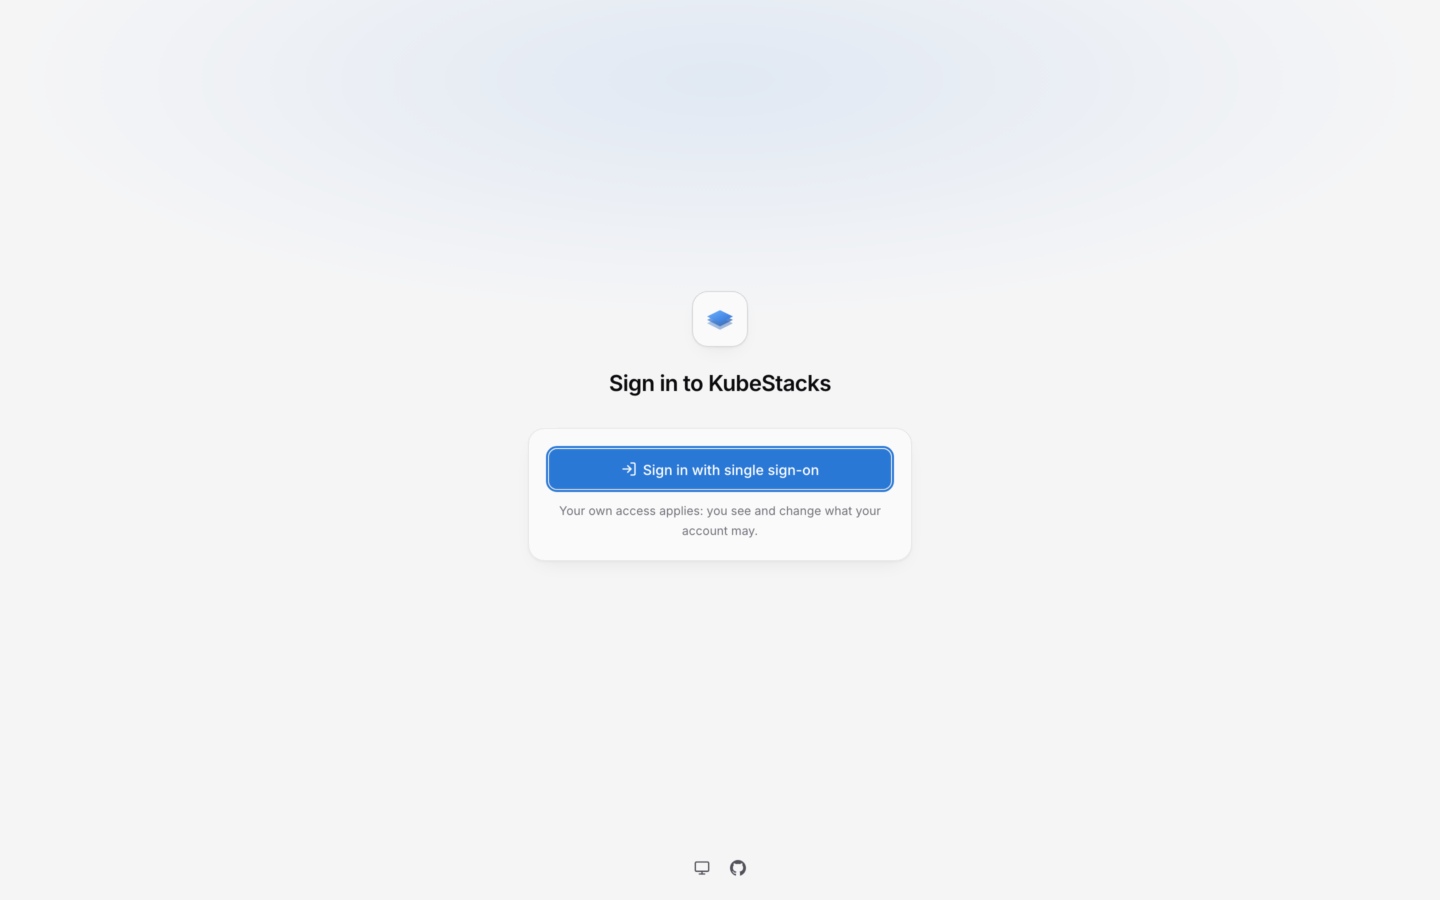
 Paste a bearer token the cluster accepts, and choose **Sign in**. You see and change what that token allows, as `kubectl` would with it.
Your team may give you a token, or you can make one with access you already have. A service account's, for example:
```bash theme={"theme":{"light":"github-light","dark":"github-dark-default"}}
kubectl create token NAME --namespace NAMESPACE
```
Tokens expire. When yours does, or is revoked, the session ends and KubeStacks asks for another.
Some teams put KubeStacks behind a proxy that signs everyone in for the whole company. There's no KubeStacks sign-in page: once you're through the company's login, you're in.
If KubeStacks says it **doesn't know who you are**, the proxy didn't pass your name on. Ask whoever runs KubeStacks to check it.
## Who you are, and what you can do
Your initials, at the bottom of the sidebar, open a menu that shows who you're signed in as, and the groups the cluster knows you by. Your access comes from the roles bound to that name and those groups.
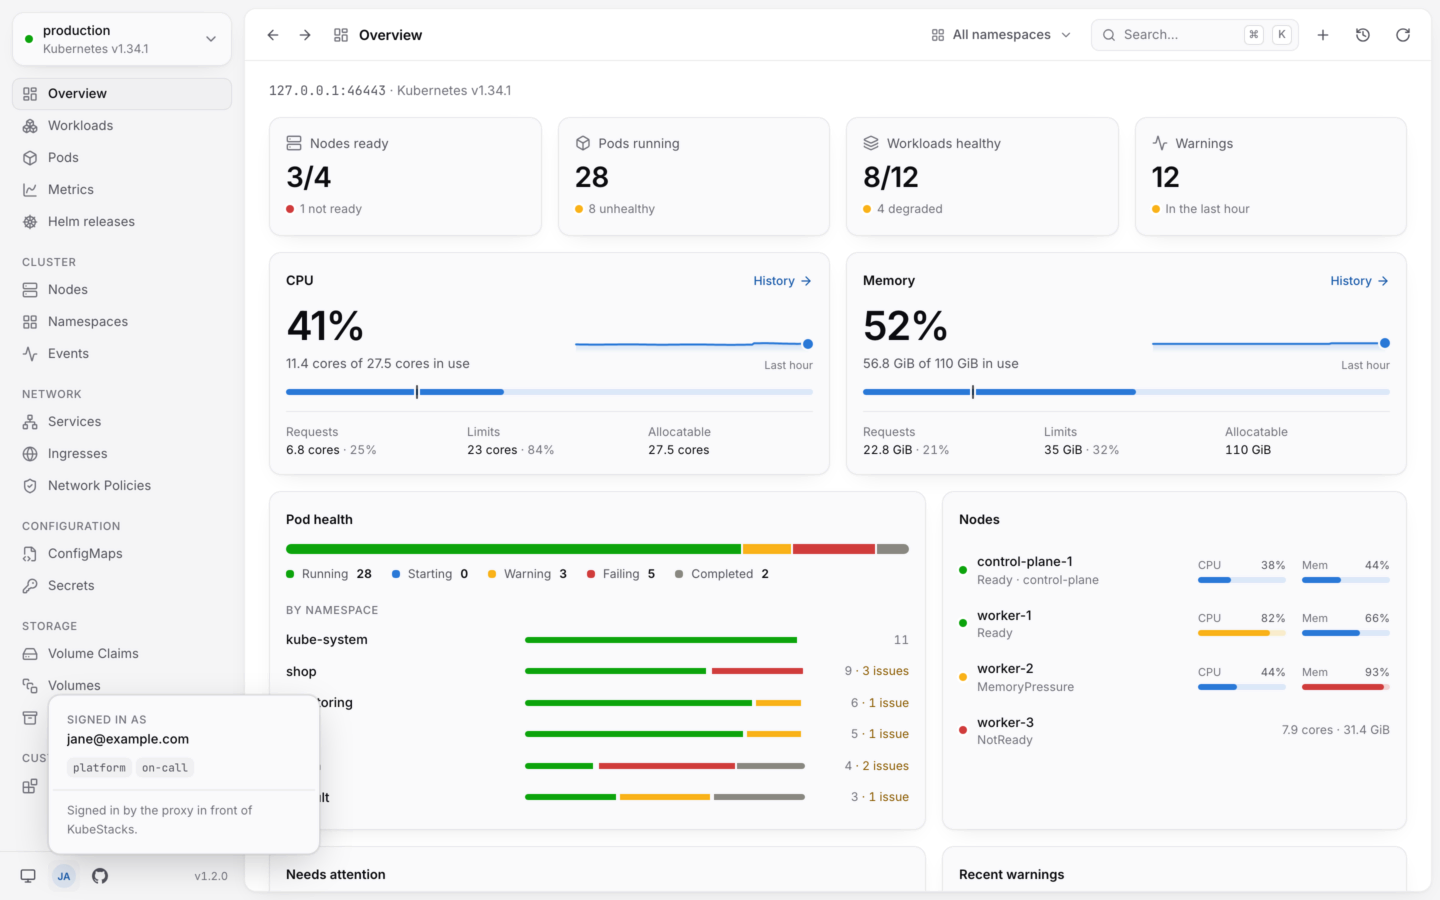
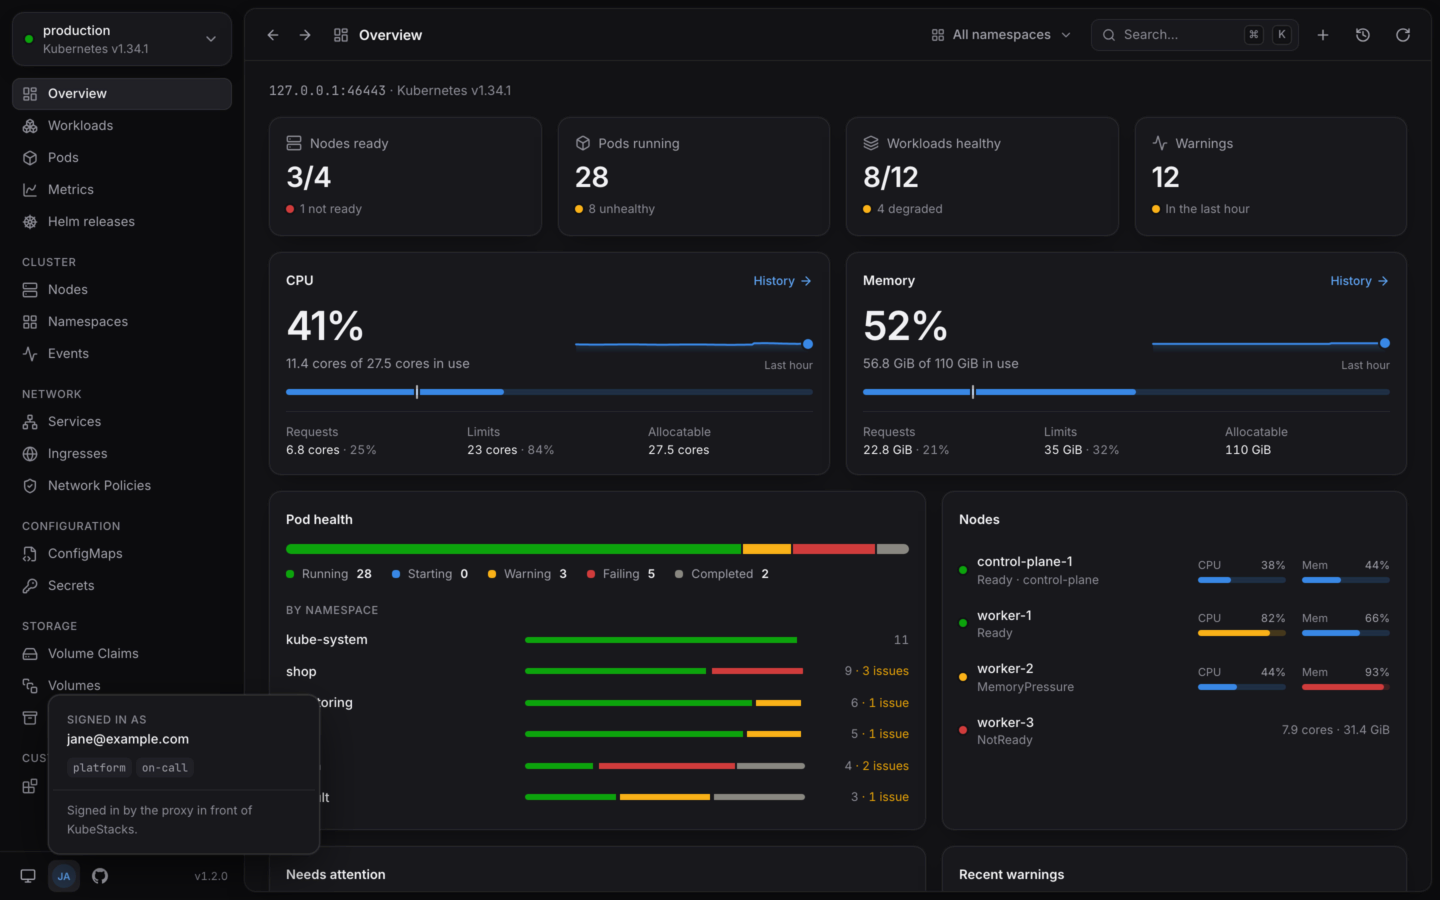 * Actions you aren't allowed to take are turned off, with the reason, like "Your account can't delete pods in shop."
* If you can only see some namespaces, pick one from the namespace menu, or type its name.
* **Sign out** is in the same menu. Behind a company login, it signs you out of the proxy, if your team set that up.
## Good to know
Every page has its own address: a pod, a filtered list, a Helm release. Copy it from the address bar and send it. Whoever opens it signs in, and sees it if their account may.
A session lasts 12 hours unless your team changed that. It also ends when KubeStacks restarts, after an upgrade say. You come back to the sign-in page, and land where you were. Behind a company login, KubeStacks keeps no session of its own: the proxy decides when you sign in again.
A banner says **Reconnecting to KubeStacks…**, and the page keeps what it showed. It picks up again as soon as the server answers. If it goes on, the server may be down, or a proxy in front of it may not pass WebSockets.
The theme, whether you've made the cluster read-only for yourself, and where usage history comes from are kept in your browser. Changing them doesn't affect anyone else.
Browsers keep ⌘N and ⌘1…6 for themselves. The command palette (⌘K, or CtrlK on Windows and Linux) has those commands. Everything else is the same as in the [desktop app](/reference/keyboard-shortcuts).
Five minutes through the app's main ideas.
What KubeStacks checks before it changes anything.
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.